OperationalImpact
Every command traced from source to endpoint, so cyber events are understood the way operators understand the process, not as security abstractions.
One language for security and operations.
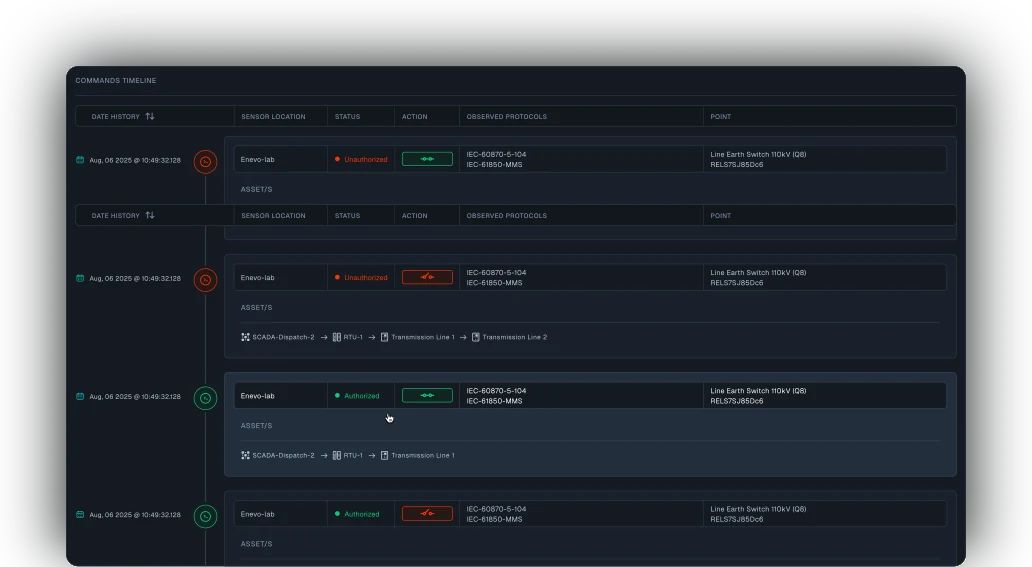
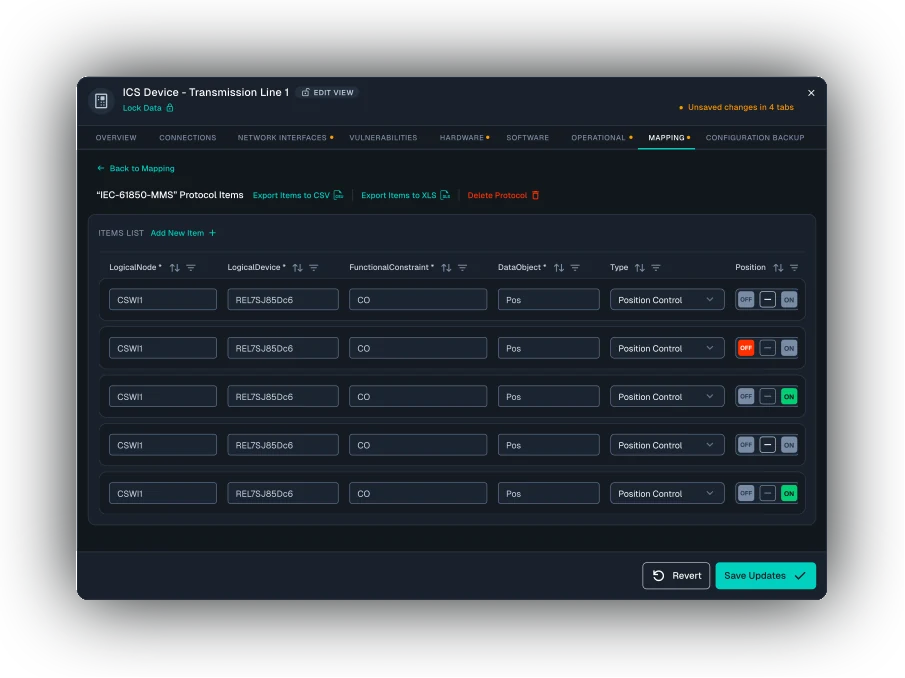
Every command is presented with the context an operator recognises: location, protocol, action, and affected point. Security analysts and process teams read the same picture and act on it together.
The process, not just the network.
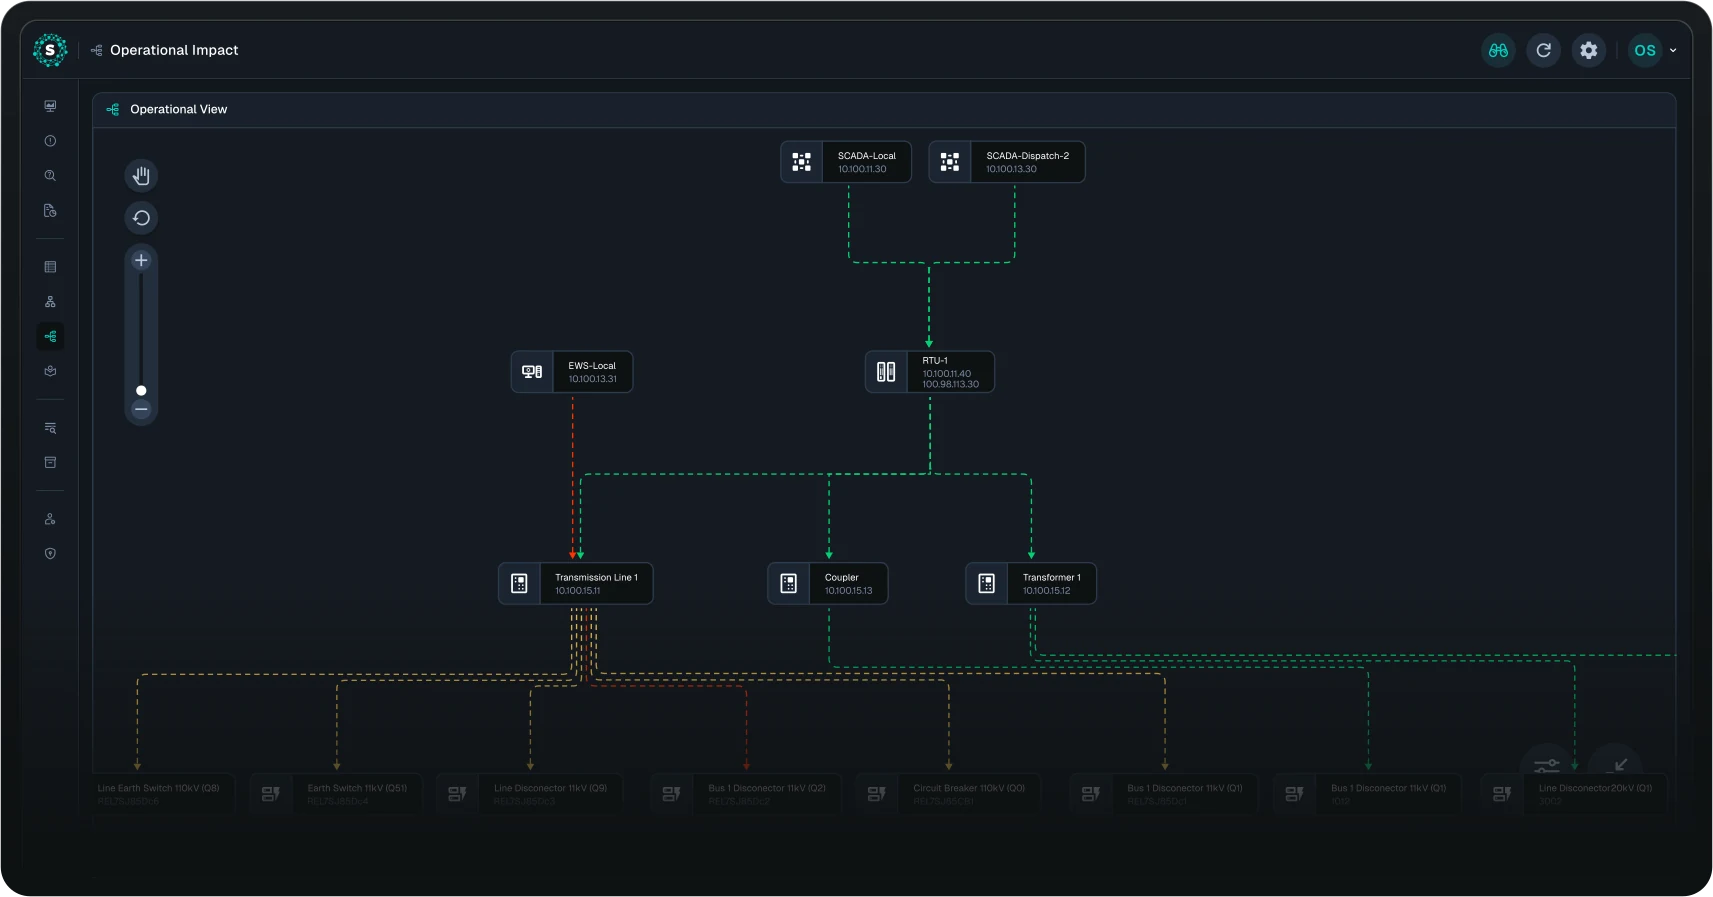
Command activity is mapped from origin to destination across the process hierarchy, showing the reach and direction of each command and which parts of the process it touched.
Unexpected activity stands out at once.
Authorised and unauthorised commands are visually separated, so deviations from normal operation surface without manual filtering.
From a single command to its full consequence.
Individual commands or batches can be selected and followed along their execution path, confirming which assets were involved and where the impact landed.
Outcome
The IT-OT gap closed. Every cyber event is understood in process terms: the commands issued, the assets reached, and their authorisation status, so response is based on operational impact.
Explore other features
- Asset InventoryA live map of every asset, down to firmwareExplore this feature
- Real Time MonitoringContinuous detection across every OT assetExplore this feature
- Incident InvestigationFull context on every event, from alert to physical impactExplore this feature
- Case ManagementFrom alerts to one defensible caseExplore this feature
See it on your own network
Your OT is in scope.Make it defensible.
Get in touch for a live walkthrough of the platform, adapted to your sector and your sites.