IncidentInvestigation
Every event traced across time and topology — correlated, contextualised, and followed through to operational impact.
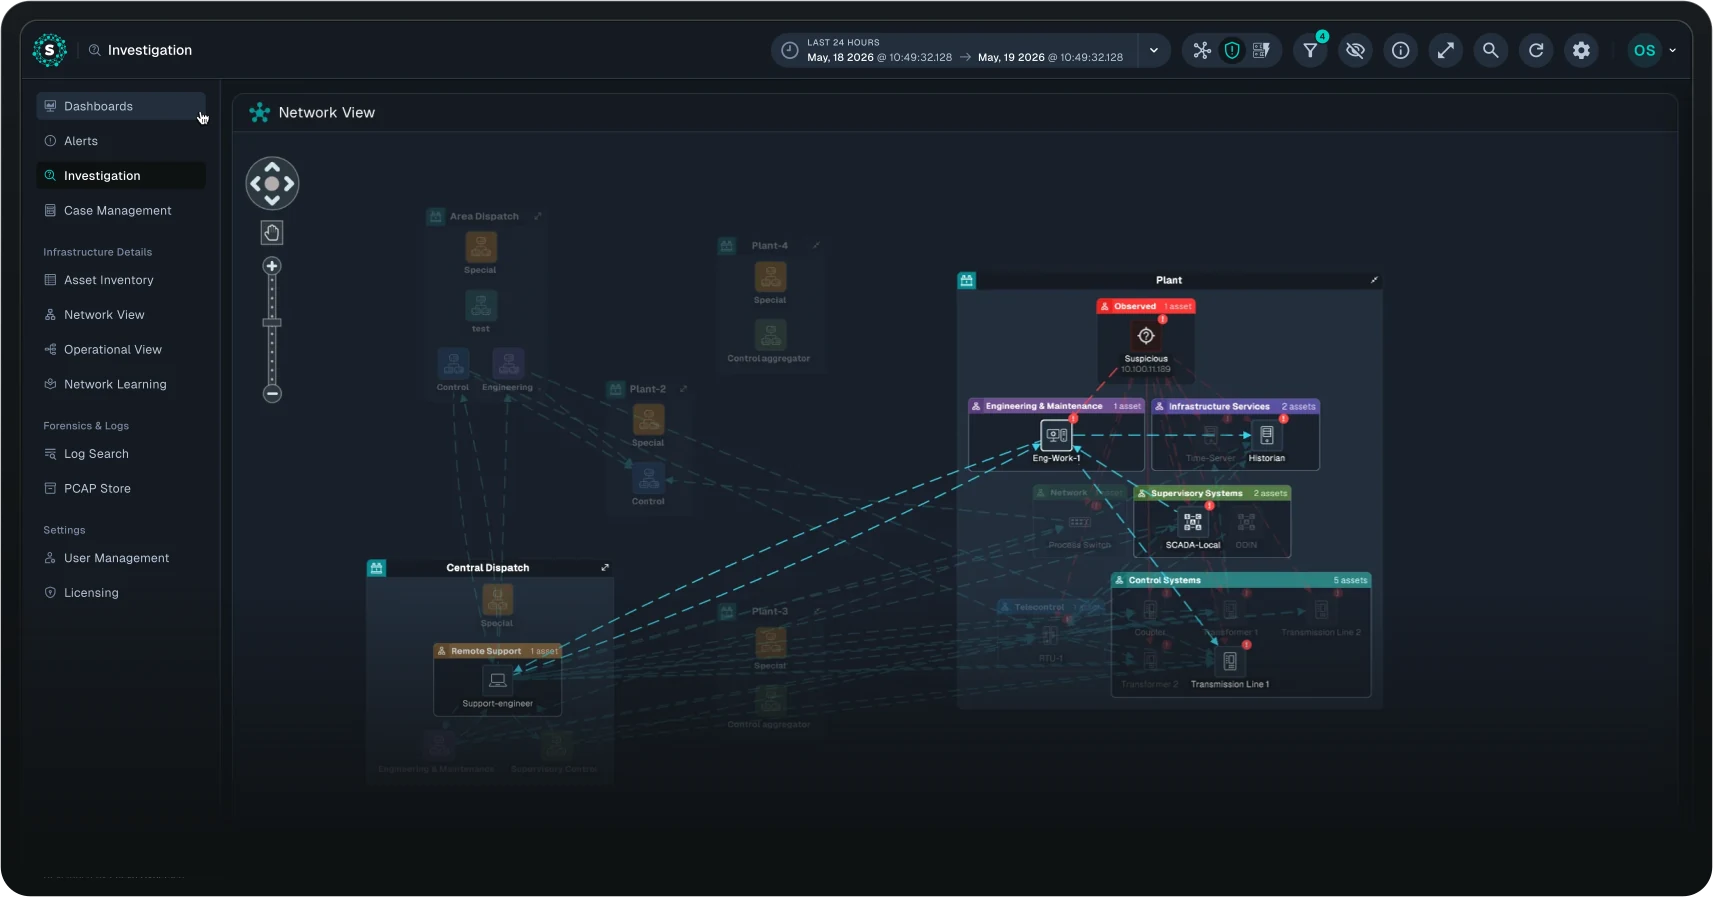
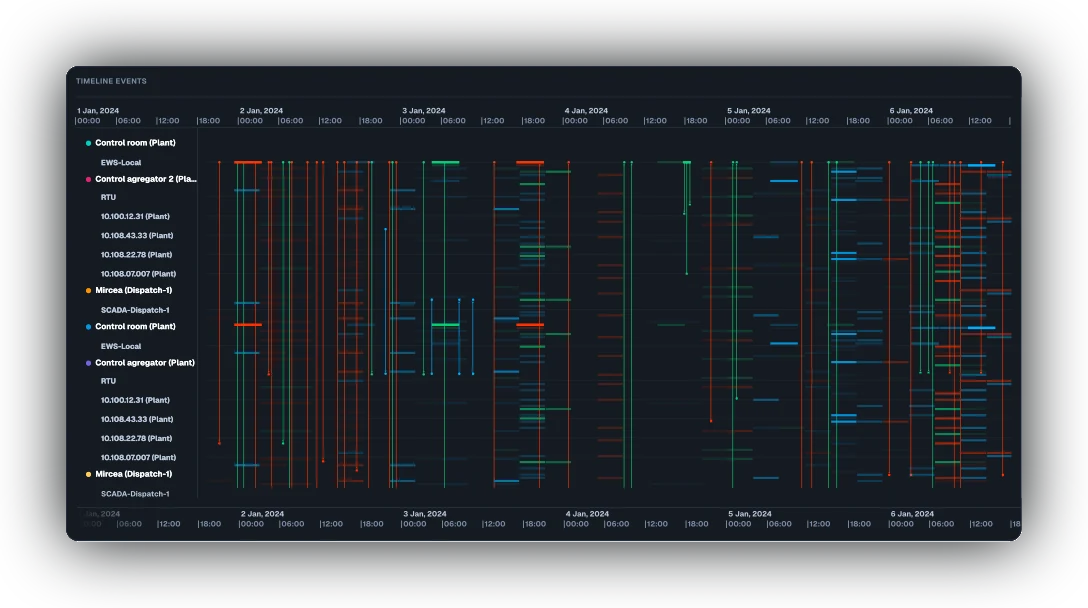
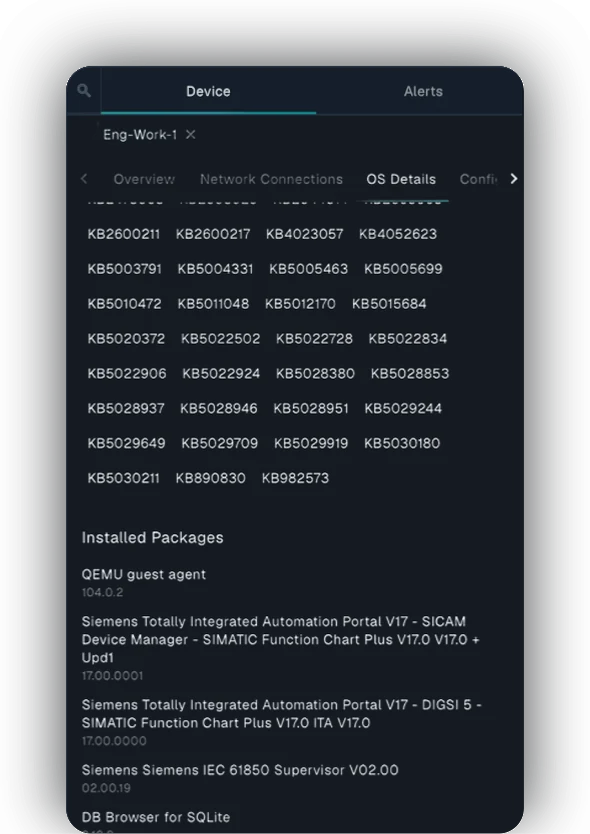
Time and topology in one view.
Alerts and commands appear together on a shared timeline, mapped against the network, showing how an incident evolves, which assets are involved, and what it means operationally.
Suspicious activity spotted in seconds.
Unauthorised commands stand out immediately, so analysts recognise a malicious sequence before spending time on filters and queries.
Faster root cause, without losing the big picture.
Analysts can focus on individual events while the wider pattern stays in view, shortening the path from first signal to confirmed cause.
Reporting without the paperwork.
Incident evidence is ready the moment the investigation ends, saving hours of manual assembly and supporting compliance and stakeholder requirements.
Outcome
Incidents understood end to end, from first signal to operational impact, in hours instead of days, with the evidence ready to report.
Explore other features
- Asset InventoryA live map of every asset, down to firmwareExplore this feature
- Real Time MonitoringContinuous detection across every OT assetExplore this feature
- Operational ImpactCyber events understood in operational termsExplore this feature
- Case ManagementFrom alerts to one defensible caseExplore this feature
See it on your own network
Your OT is in scope.Make it defensible.
Get in touch for a live walkthrough of the platform, adapted to your sector and your sites.